
Calvatis GmbH
Calvatis GmbH
Group
Aurora
Discovered
2026-11-20 18:47 UTC
Est. attack date
2026-11-20
Country

Sector
Agriculture and Food Production
Education
Energy & Utilities
Financial Services
Government & Defense
Healthcare
Hospitality
Manufacturing
Other
Professional Services
Retail & E-Commerce
Technology
Transportation
Description:
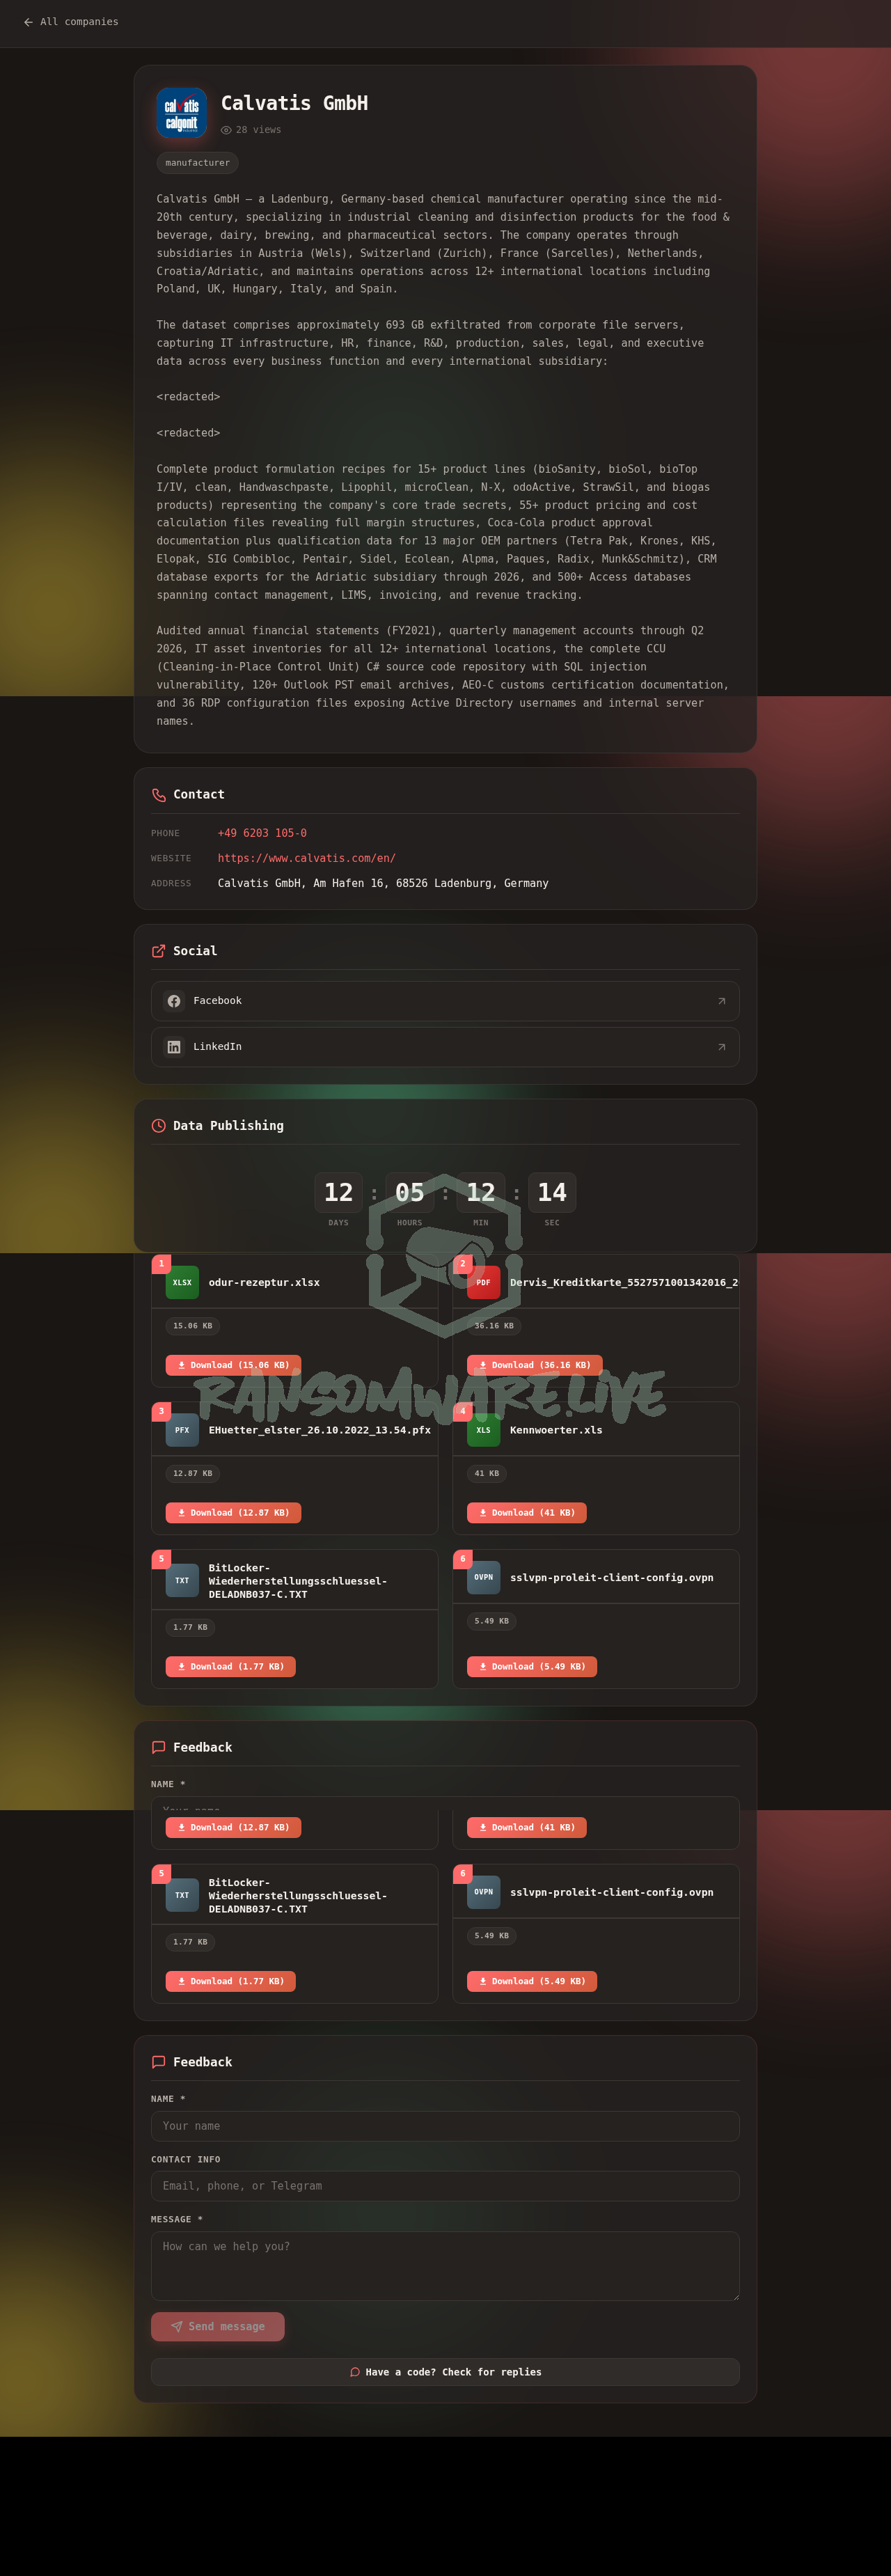
[manufacturer] Calvatis GmbH — a Ladenburg, Germany-based chemical manufacturer operating since the mid-20th century, specializing in industrial cleaning and disinfection products for the food & beverage, dairy, brewing, and pharmaceutical sectors. The company operates through subsidiaries in Austria (Wels), Switzerland (Zurich), France (Sarcelles), Netherlands, Croatia/Adriatic, and maintains operations across 12+ international locations including Poland, UK, Hungary, Italy, and Spain.
The dataset comprises approximately 693 GB exfiltrated from corporate file servers, capturing IT infrastructure, HR, finance, R&D, production, sales, legal, and executive data across every business function and every international subsidiary:
<redacted>
<redacted>
Complete product formulation recipes for 15+ product lines (bioSanity, bioSol, bioTop I/IV, clean, Handwaschpaste, Lipophil, microClean, N-X, odoActive, StrawSil, and biogas products) representing the company's core trade secrets, 55+ product pricing and cost calculation files revealing full margin structures, Coca-Cola product approval documentation plus qualification data for 13 major OEM partners (Tetra Pak, Krones, KHS, Elopak, SIG Combibloc, Pentair, Sidel, Ecolean, Alpma, Paques, Radix, Munk&Schmitz), CRM database exports for the Adriatic subsidiary through 2026, and 500+ Access databases spanning contact management, LIMS, invoicing, and revenue tracking.
Audited annual financial statements (FY2021), quarterly management accounts through Q2 2026, IT asset inventories for all 12+ international locations, the complete CCU (Cleaning-in-Place Control Unit) C# source code repository with SQL injection vulnerability, 120+ Outlook PST email archives, AEO-C customs certification documentation, and 36 RDP configuration files exposing Active Directory usernames and internal server names.
Exposure Report
by ParanoidLab0
Passwords
0 critical
0
Cookies
0 critical
Last queried 2026-11-20 18:47 UTC
Leak Screenshot:
Other recent victims
Same group: Aurora
-
 TraWell Co S.p.A. (d/b/a Safe Bag)
2026-11-20
-
 William Cook Holdings Limited
2026-11-20
-
Boutinot Limited
2026-11-19
Same sector: Professional Services
-
 BK Law Group LLC
2026-11-20
-
relyonmsi.com
2026-11-20
-
Jones Walker
2026-11-20
-
 Barapp Law Firm
2026-11-20
-
Rudolph F. Jass, Jr., PLLC
2026-11-19
Same country: Germany
-
OSWALD Elektromotoren GmbH
2026-11-19
-
Scooter Autoservice gmbh
2026-11-18
-
roedentallab.com
2026-11-17
-
WWGlas
2026-11-17
-
Rosenberger Legal
2026-11-17
Legal Disclaimer: Ransomware.live does not engage in the acquisition, exfiltration, downloading, possession, hosting, access, consultation, redistribution, or disclosure of unlawfully obtained data. This platform indexes only publicly visible information posted by ransomware operators and open web sources without accessing or obtaining the underlying stolen content. The service is provided to support public awareness, legitimate research, and cyber-resilience. No stolen personal or confidential data is collected or distributed via this site.