
GreenbergFarrow
GreenbergFarrow
Group
Aurora
Discovered
2026-10-27 12:11 UTC
Est. attack date
2026-10-27
Sector
Agriculture and Food Production
Education
Energy & Utilities
Financial Services
Government & Defense
Healthcare
Hospitality
Manufacturing
Other
Professional Services
Retail & E-Commerce
Technology
Transportation
Description:
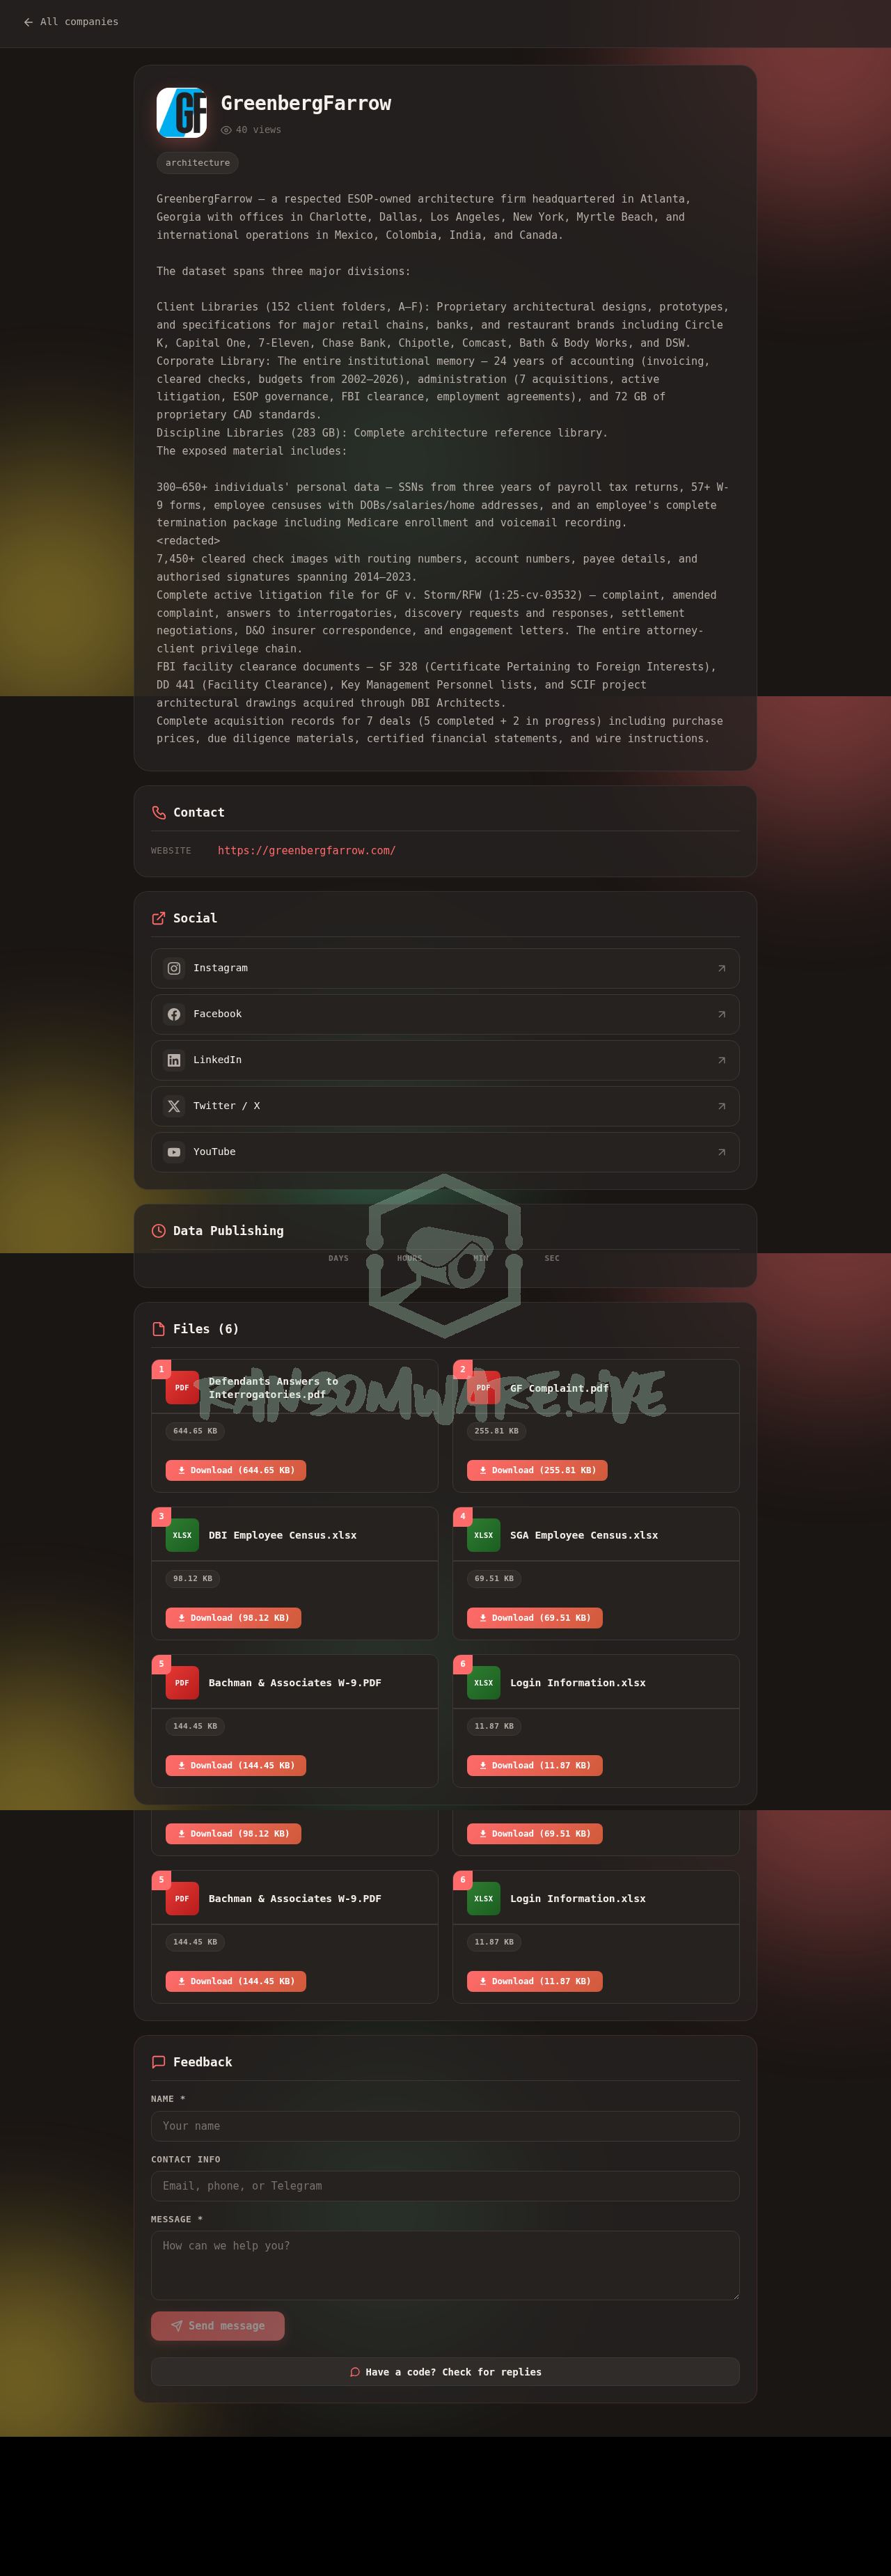
[architecture] GreenbergFarrow — a respected ESOP-owned architecture firm headquartered in Atlanta, Georgia with offices in Charlotte, Dallas, Los Angeles, New York, Myrtle Beach, and international operations in Mexico, Colombia, India, and Canada.
The dataset spans three major divisions:
Client Libraries (152 client folders, A–F): Proprietary architectural designs, prototypes, and specifications for major retail chains, banks, and restaurant brands including Circle K, Capital One, 7-Eleven, Chase Bank, Chipotle, Comcast, Bath & Body Works, and DSW.
Corporate Library: The entire institutional memory — 24 years of accounting (invoicing, cleared checks, budgets from 2002–2026), administration (7 acquisitions, active litigation, ESOP governance, FBI clearance, employment agreements), and 72 GB of proprietary CAD standards.
Discipline Libraries (283 GB): Complete architecture reference library.
The exposed material includes:
300–650+ individuals' personal data — SSNs from three years of payroll tax returns, 57+ W-9 forms, employee censuses with DOBs/salaries/home addresses, and an employee's complete termination package including Medicare enrollment and voicemail recording.
<redacted>
7,450+ cleared check images with routing numbers, account numbers, payee details, and authorised signatures spanning 2014–2023.
Complete active litigation file for GF v. Storm/RFW (1:25-cv-03532) — complaint, amended complaint, answers to interrogatories, discovery requests and responses, settlement negotiations, D&O insurer correspondence, and engagement letters. The entire attorney-client privilege chain.
FBI facility clearance documents — SF 328 (Certificate Pertaining to Foreign Interests), DD 441 (Facility Clearance), Key Management Personnel lists, and SCIF project architectural drawings acquired through DBI Architects.
Complete acquisition records for 7 deals (5 completed + 2 in progress) including purchase prices, due diligence materials, certified financial statements, and wire instructions.
Exposure Report
by ParanoidLab0
Passwords
0 critical
0
Cookies
0 critical
Last queried 2026-10-27 12:11 UTC
Leak Screenshot:
Other recent victims
Same group: Aurora
-
 Ernesto Malvestiti S.p.A.
2026-10-26
-
 ARX Group SA
2026-10-23
-
 Allmand-Smith Limited
2026-10-21
-
 Duarte Nursery, Inc.
2026-10-20
-
POWERsonic Industries Inc.
2026-10-19
Same sector: Professional Services
-
Morrison Cohen
2026-10-26
-
Beasley Allen Law Firm
2026-10-26
-
Smith Feddeler & Smith
2026-10-26
-
THOMAS JORDAN, P.A
2026-10-26
Legal Disclaimer: Ransomware.live does not engage in the acquisition, exfiltration, downloading, possession, hosting, access, consultation, redistribution, or disclosure of unlawfully obtained data. This platform indexes only publicly visible information posted by ransomware operators and open web sources without accessing or obtaining the underlying stolen content. The service is provided to support public awareness, legitimate research, and cyber-resilience. No stolen personal or confidential data is collected or distributed via this site.